
Platform Architecture Overview
High-level technical overview of blackLen's distributed topology, frontend client application, API gateway, and data boundary model.
blackLen is engineered with a modular, decoupled architecture designed for high throughput, strict tenant isolation, and responsive operator user experience.
Architectural Blueprint: One Unified Workspace
The blackLen platform unifies scoped penetration testing, live checklist execution, payload management, and team collaboration within isolated workspace boundaries.
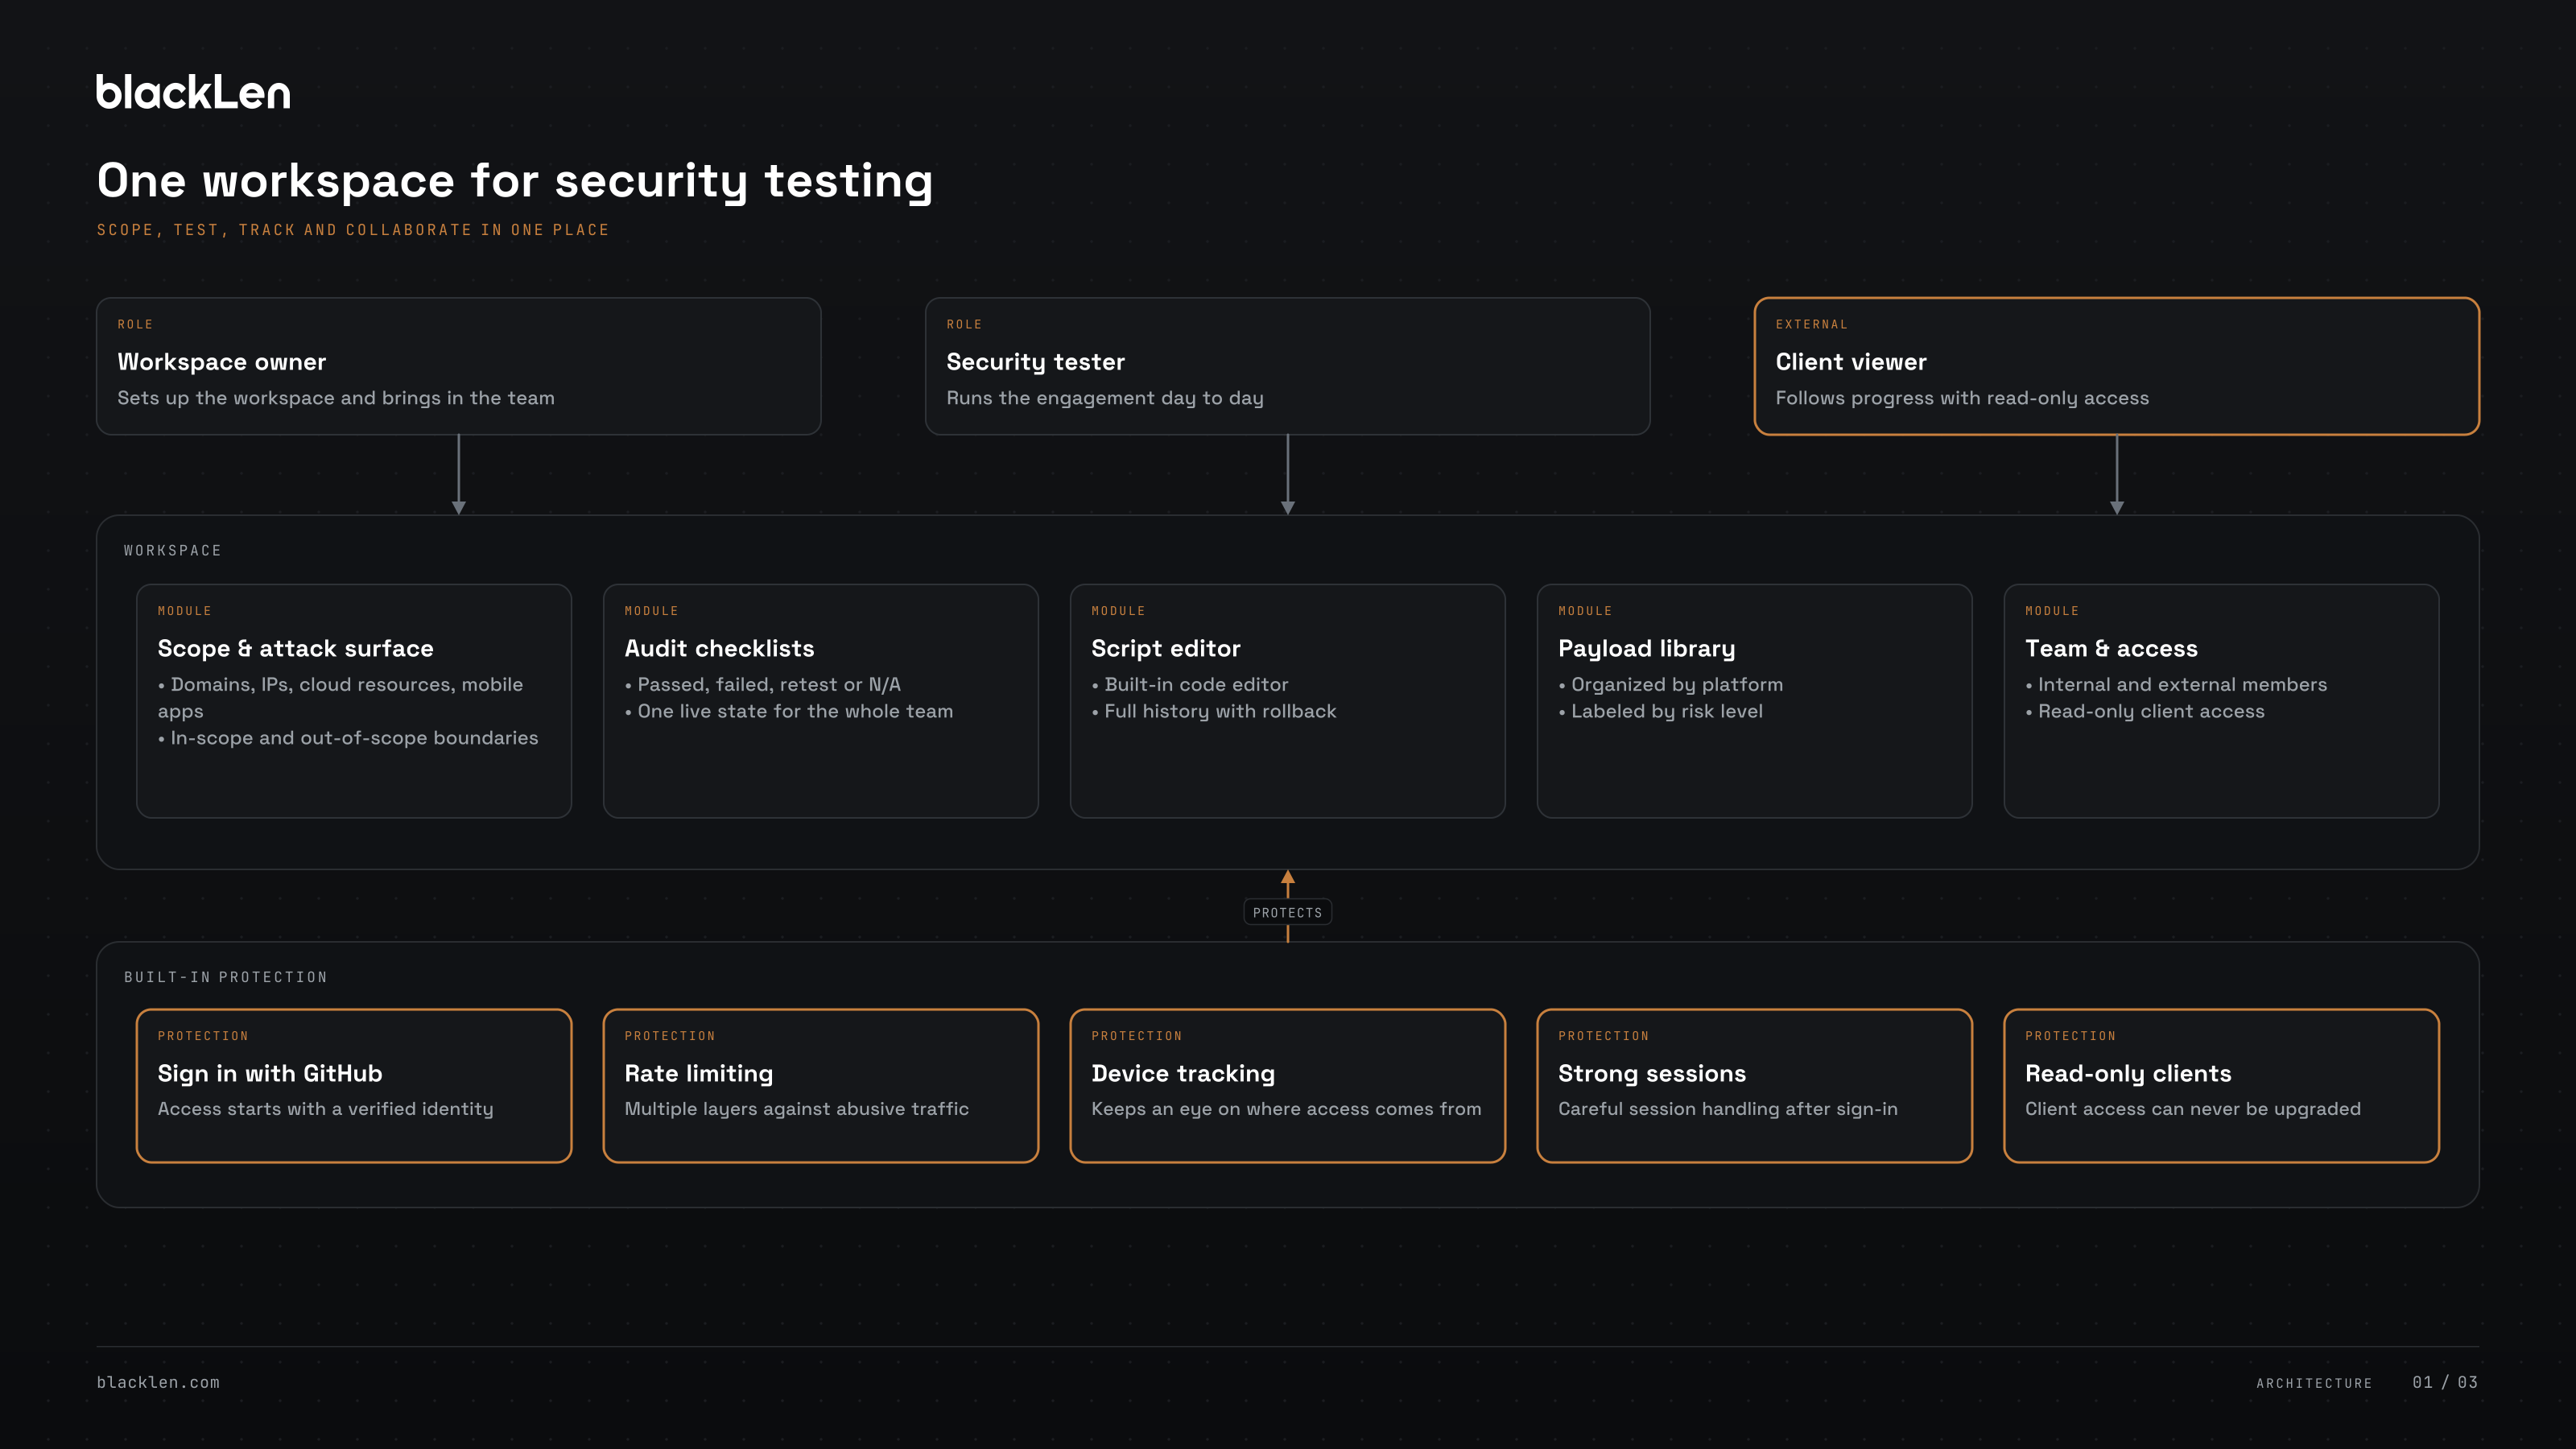
Key Blueprint Components:
- Role Isolation: Granular RBAC supporting Workspace Owners, Security Testers, and Read-Only Client Viewers.
- Integrated Tooling: In-browser custom script authoring, attack surface asset scoping, and real-time finding logs.
- Perimeter Defense: Multi-vector throttles, hardware device fingerprinting, and strict token management.
Ingress Topology & Subdomain Routing
The platform is partitioned across dedicated subdomains:
- Marketing & Technical Documentation (
blacklen.com): Public landing pages, feature tours, sitemaps, and technical documentation. - Operator Workspace Application (
app.blacklen.com): High-velocity Single Page Application (SPA) where security teams manage organizations, projects, checklists, scripts, and payloads. - REST API Gateway (
api.blacklen.com): Centralized backend handling authentication, object-level RBAC evaluation, data persistence, and rate limiting.
Concentric Defense-in-Depth
Security in blackLen is structured in concentric rings, ensuring that compromise or misconfiguration of one layer cannot breach the core tenant data.
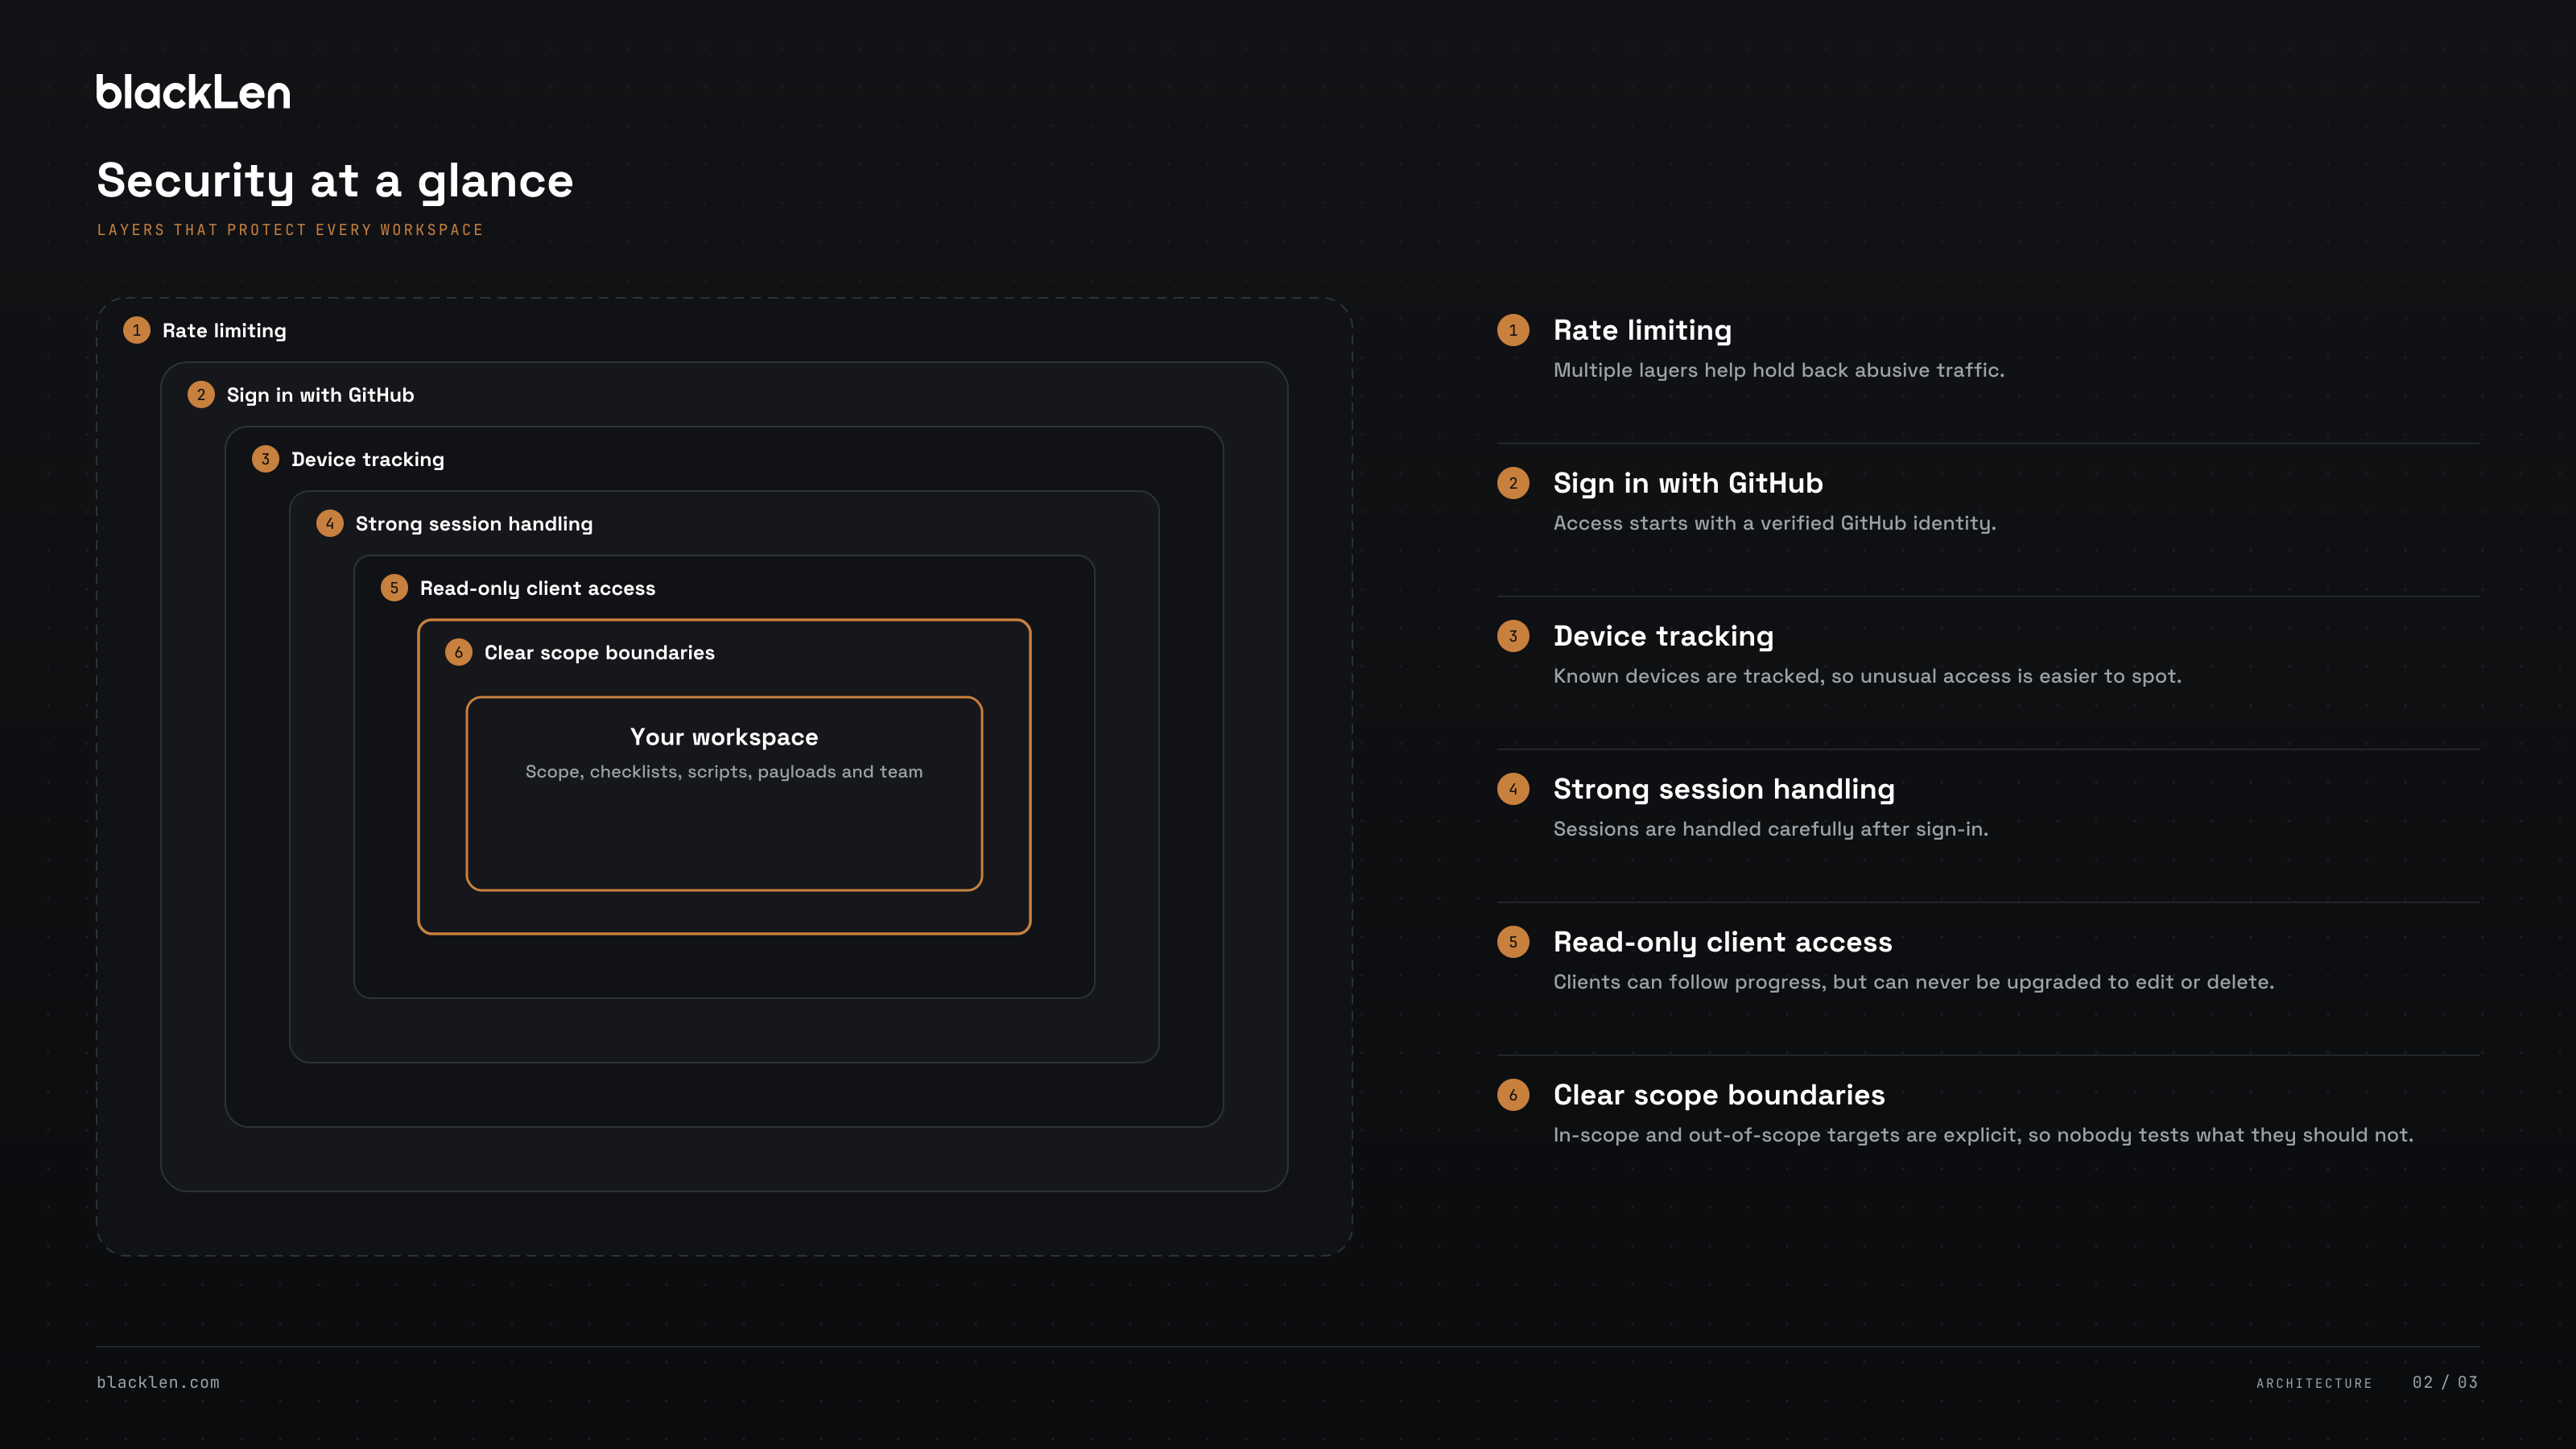
- Identity & Authentication: Verified GitHub OAuth & TOTP 2FA.
- Traffic Throttling: Multi-vector Redis rate limiting.
- Session Integrity: Web Locks API cross-tab synchronization & device fingerprint validation.
- Scope Boundaries: Hard object-level checks on all project data.
- Client Isolation: Read-only tokens for external stakeholders and auditors.
Frontend & Client Architecture
The operator workspace frontend is designed for fast, frictionless security workflows:
- Core Framework: React 19 built with Vite 7 for rapid compilation and minimal asset footprints.
- State Management: Redux Toolkit managing active organization contexts, project states, and notification channels.
- Embedded Script Engine: Integrated Monaco Editor powering in-browser custom script authoring and version history inspection.
- Token Management: Client-side credential management with automated token refreshing across active browser tabs.
Live Team Synchronization & Script Versioning
Multiple operators can collaborate in real time on the same project without race conditions or state desynchronization.
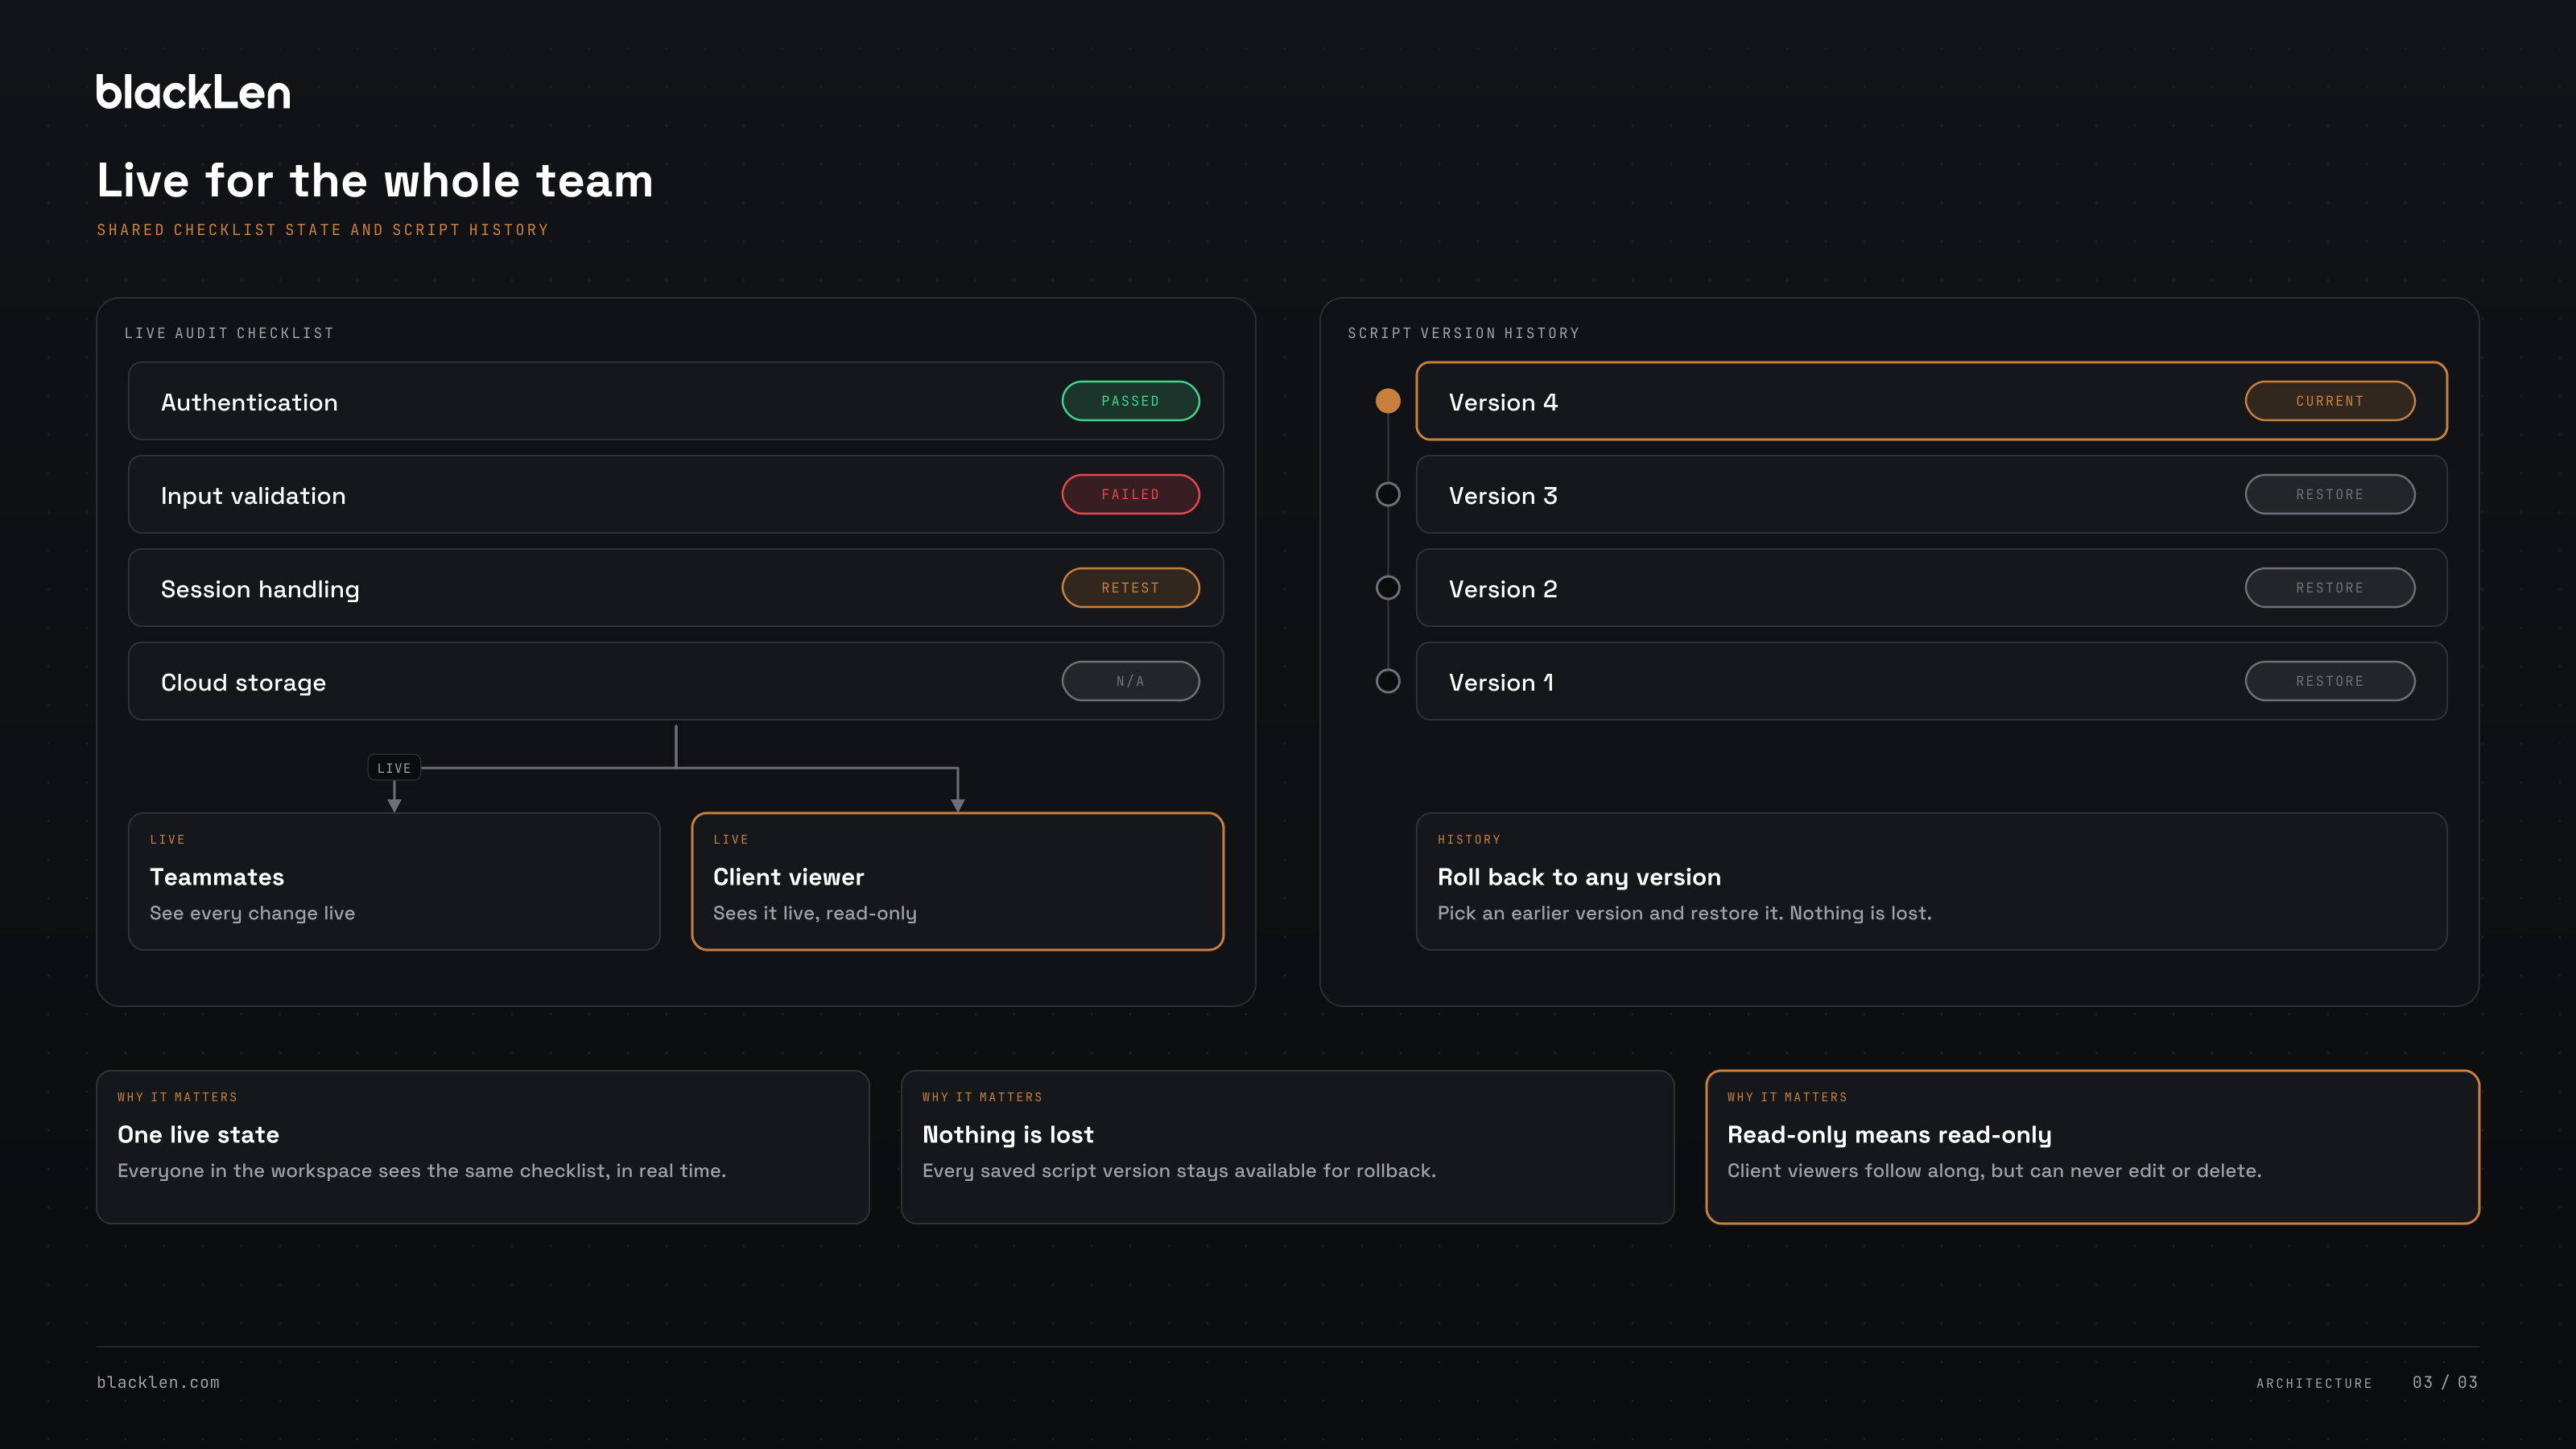
- Checklist Sync: Live status updates and finding evidence immediately broadcast to team members and client viewers.
- Script Rollback: Monaco editor version checkpoints allow instant diffing and rolling back to historical script executions.
Backend API & Storage Engine
The platform backend exposes a unified RESTful API:
- Framework: Django REST Framework (DRF) providing serializer validations, transactional integrity, and object-level permission enforcement.
- Relational Storage: PostgreSQL storing user accounts, organization memberships, projects, attack surface assets, checklist items, and versioned scripts.
- Cache & Rate-Limiting: Redis providing caching, session concurrency coordination, and multi-vector rate limiting.
Two-Tier Boundary Separation
Data in blackLen is strictly partitioned across two architectural tiers:
-
Tier 1: Organization Governance:
- Controls organization profile, member invitations, role management, and global resource libraries (tools, script templates, payload collections).
- Bound to the
Organizationentity.
-
Tier 2: Project Engagement:
- Isolates specific security assessments, penetration tests, or red team exercises.
- All scoped assets, active checklist execution states, and findings live exclusively inside the project boundary.
- Bound to the
Projectentity with independent project-level membership roles.